M-XDR
90+ Integrations
Managed Extended Detection & Response
M-XDR + SIEM + SOAR + SOC — Unified. Managed. Always On.
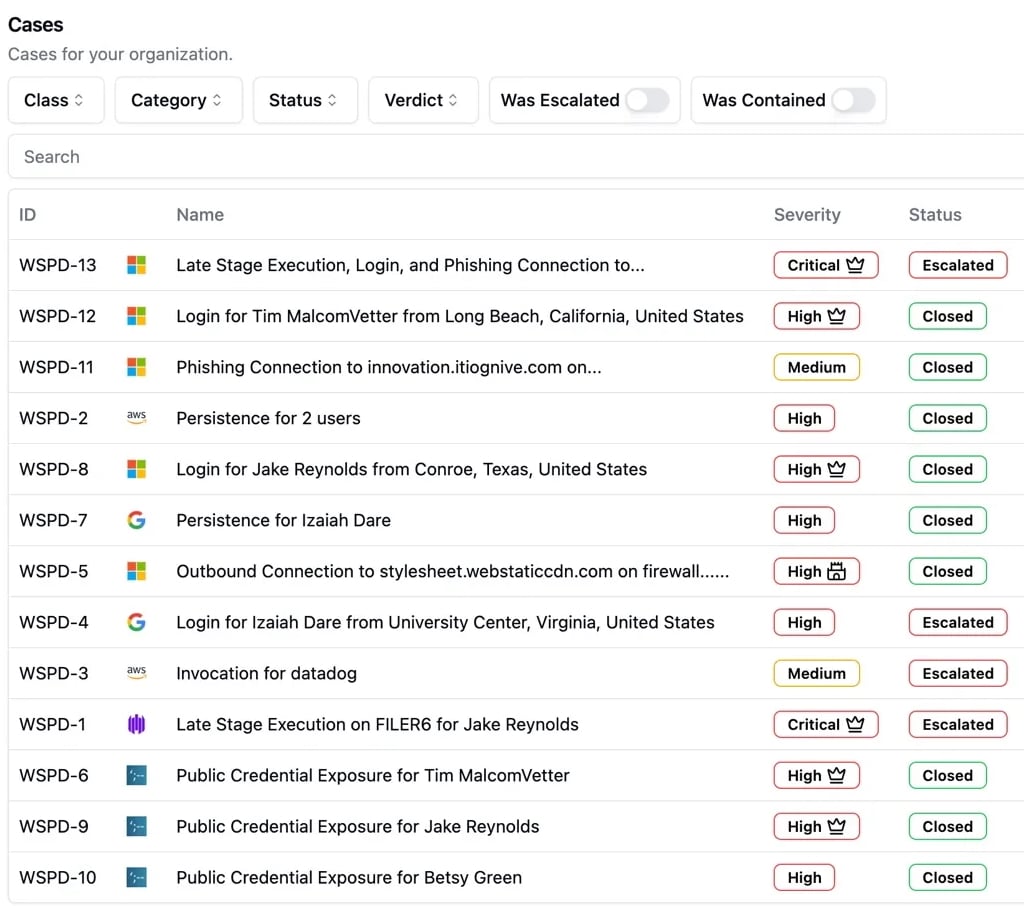
ShieldWatch XDR is a comprehensive Extended Detection and Response platform designed to unify threat detection, response, and compliance monitoring in one integrated solution.
With a fusion of advanced AI-driven analytics, 24/7 SOC monitoring, and real-time orchestration capabilities.
Unified Platform
All-In-One Security Architecture
90+ Integrations
Managed Extended Detection & Response
500+ Detections
Security Information & Event Management
150+ Workflows
Security Orchestration, Automation & Response
24/7 Monitoring
US-Based Security Operations Center

“ShieldWatch has been an exceptional partner in guiding our organization through the complex process of merging five companies into one—where cybersecurity was a top priority. ShieldWatch XDR delivered immediate and measurable results.”
Joe Klemballa
Director of IT & Security, ServicePoint
Four layers of defense, one platform, threats killed in seconds.
Managed Extended Detection & Response
End-to-end threat detection across endpoints, cloud, network, identity, and email — managed 24/7. Millisecond verdicts. Automated containment. Full-stack visibility.
Security Information & Event Management
Centralized log ingestion and correlation across your entire environment. AI-powered analytics surface real threats from billions of events — reducing false positives by up to 90%.
Security Orchestration, Automation & Response
150+ pre-built automated playbooks handle containment, escalation, and remediation without manual intervention. Integrated ChatOps enables real-time collaboration when human judgment is needed.
U.S.-based certified analysts monitoring your environment around the clock. Expert triage, proactive threat hunting, and incident response — staged within 30 minutes of a declared incident.
ShieldWatch XDR is ShieldWatch’s comprehensive Extended Detection and Response platform designed to unify threat detection, response, and compliance monitoring in one integrated solution. With a fusion of advanced AI-driven analytics, 24/7 SOC monitoring, and real-time orchestration capabilities, ShieldWatch empowers organizations to identify and neutralize threats before they can impact operations.
See how the unified ShieldWatch platform compares across essential security capabilities.
ShieldWatch Score: 14/14
| Features & Capabilities | ||||||
|---|---|---|---|---|---|---|
| True Multi-Layer, Multi-Tenant Architecture | Full Support | Full Support | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost |
| Unified Cyber Defense Platform (NG-SIEM, ITDR, SOAR, UEBA, Threat Intel) | Full Support | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost |
| All Core Capabilities Bundled in One License — No Hidden Fees | Full Support | Not Available | Not Available | Not Available | Not Available | Not Available |
| Free Deployed Sensors — 24/7 Coverage Without Extra Charges | Full Support | Not Available | Not Available | Not Available | Not Available | Not Available |
| Remote Edge Monitoring & Distributed Data Collection | Full Support | Partial / Additional Cost | Full Support | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost |
| Rapid Deployment — Fully Operational In Hours, Not Days | Full Support | Not Available | Partial / Additional Cost | Not Available | Not Available | Not Available |
| Lightweight Footprint — Minimal Infrastructure Impact | Full Support | Partial / Additional Cost | Full Support | Not Available | Partial / Additional Cost | Not Available |
| Complete Attack Surface Visibility — Cloud, Endpoint, Network, Users | Full Support | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost |
| Integrated ChatOps for Real-Time Event Verification | Full Support | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost |
| Compliance-Ready by Design (SOC 2, HIPAA, ISO 27001) | Full Support | Partial / Additional Cost | Partial / Additional Cost | Full Support | Partial / Additional Cost | Partial / Additional Cost |
| On-Demand Incident Response (Stage Within 30 Minutes) | Full Support | Partial / Additional Cost | Partial / Additional Cost | Not Available | Partial / Additional Cost | Not Available |
| Pre-Built, Automated SOAR Workflows (150+ Out-of-Box Playbooks) | Full Support | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost |
| Robust Integration Ecosystem (50+ Integrations) | Full Support | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost | Partial / Additional Cost | Full Support |
| Natural Language Search & Query — Analyst-Friendly | Full Support | Partial / Additional Cost | Partial / Additional Cost | Not Available | Partial / Additional Cost | Not Available |
Empower your security team with AI-driven automation, intelligent threat detection, and seamless collaboration to stay ahead of evolving cyber threats.
ShieldWatch Agentic AI operates inside your XDR environment as an autonomous cyber analyst. It continuously correlates telemetry, prioritizes real threats, and initiates containment actions in seconds.
Our AI works alongside our 24/7 SOC analysts to deliver precision at scale. Machine speed meets human judgment, with complex incidents escalated using full context and enriched intelligence.
ShieldWatch leverages 150+ SOAR workflows to automate threat containment, user isolation, credential resets, ticketing, and compliance documentation.
ShieldWatch XDR delivers a comprehensive security solution with everything you need to protect your organization.
Real-time monitoring of endpoints, cloud environments (MSFT, AWS, GCP), mobile devices, email, identity systems, and networks.
Systematic phone or text alerts to users, automated containment, and immediate forensics by our security analysts—powered by out-of-the-box playbooks and orchestration.
Set up in minutes. ShieldWatch automatically investigates up to 90 days of historical logs, immediately alerting you to any latent threats.
AI-powered threat telemetry and smart correlation detect and isolate threats across your environment before they escalate.
End-to-end visibility into workstations, servers, mobile devices, and cloud tenants—giving your organization full-stack control.
Our expert team stands ready 24/7 to review, triage, and respond to alerts, offering deep forensics and policy-level remediation.
ShieldWatch XDR offers comprehensive security monitoring and response, protecting your business from evolving threats with advanced technologies.
ShieldWatch unifies threat detection, response, and compliance monitoring across endpoints, networks, cloud, and identity.
AI-driven analytics and 24/7 SOC oversight enable sub-8.5 second threat verdicts and containment actions within minutes.
Deployed and operational in minutes, the platform retroactively analyzes 90 days of historical logs.
Includes 150+ pre-built SOAR workflows out of the box, enabling consistent incident response at scale.
Machine learning and threat intelligence correlation reduce false positives by up to 90%.
Designed to support SOC 2, HIPAA, CMMC 2.0, and ISO 27001 with continuous monitoring and reporting.
Detects misconfigurations, privilege abuse, and suspicious activity across Microsoft 365, AWS, Azure, and more.
Upon a declared incident, ShieldWatch’s First Responders IR Team begins triage within 30 minutes.
How It Works
Five phases from onboarding to full compliance coverage. Built for speed, powered by AI, backed by our US-Based SOC.
Connect
Be operational in hours, not weeks.
Deployment Time: ~1 Day
Focus: Visibility, Discovery, Threat Inventory
Observe
Know what normal looks like — and spot what doesn't.
Correlate
Automated threat triage begins here.
Result: 90% reduction in false positives
ChatOps / case management for direct customer interaction
Respond
Our analysts work alongside the AI to accelerate remediation.
Comply
Security that supports your audits, too.
Built-in governance + roadmap for security maturity
Managed Detection and Response
In addition to delivering comprehensive Extended Detection and Response, the ShieldWatch XDR platform includes an integrated Security Incident and Event Management (SIEM) system. This SIEM correlates security events across your environment, enabling deeper insight and faster threat detection.
To further accelerate response, the platform also includes out-of-the-box Security Orchestration, Automation, and Response (SOAR) capabilities — empowering security teams to automate incident response workflows and reduce manual effort.
ShieldWatch XDR detects threats in minutes using 90 days of logs.
The ShieldWatch XDR platform is designed for speed and efficiency. It can be fully configured within minutes and immediately begins ingesting and analyzing 90 days of historical log data from all connected integrations.
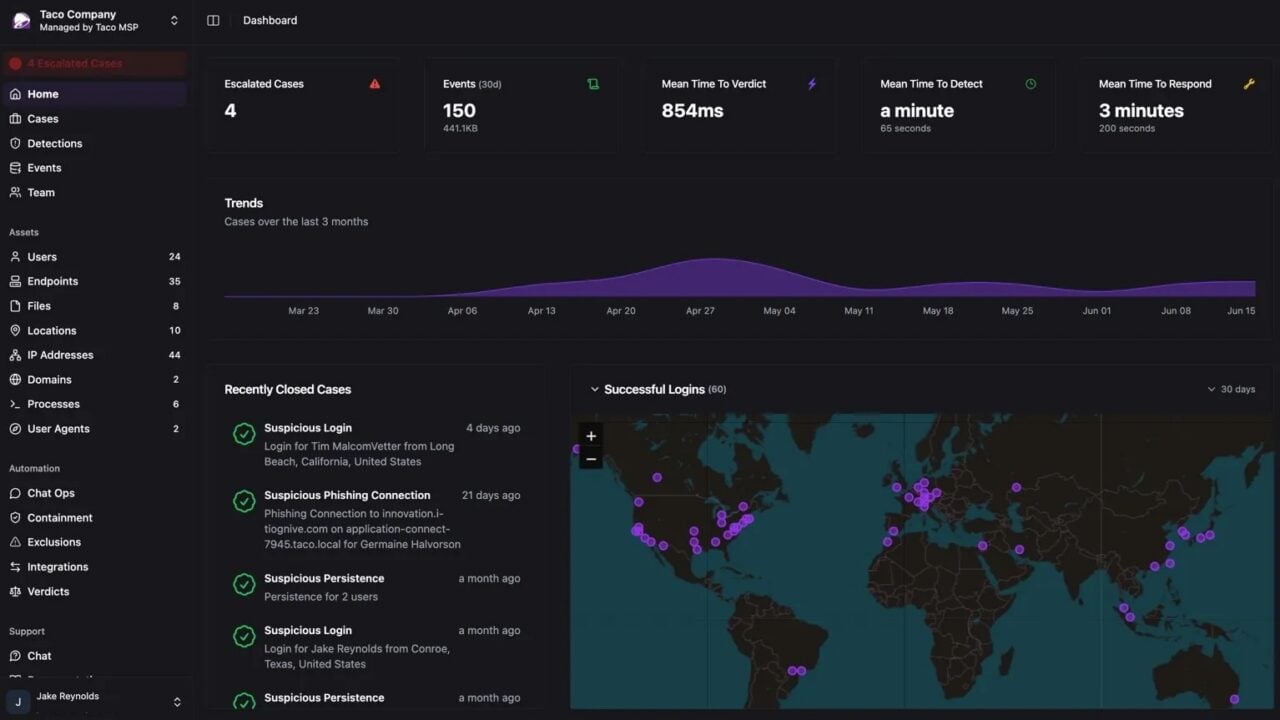
Investigate every alert 24x7x365

Triage and respond in seconds.
Unaffected by late nights, alert volume, or hallucinations.
We ping your users over Slack, Teams, Email, & SMS to discover missing context.
Keep your logs in our data lake for searching & compliance.
Onboard in minutes. We'll take it from there.
From strategy to execution, we combine expert guidance, cutting-edge technology, and tailored services to deliver a solution built around your business.
| EXPERIENCE & EXPERTISE
We have nearly 30 years of experience in managing and protecting technology infrastructures, allowing a more comprehensive approach to meeting your business, compliance, and cybersecurity needs.
| INNOVATIVE SOLUTIONS
We offer advanced capabilities curated by our forward-thinking engineers and innovative partnerships to drive industry-leading technology.
| END-TO-END CAPABILITY
Unlike many providers, we have professional expertise and services from strategy to setting up the appropriate infrastructure, security controls, and ongoing security and IT management.
| HANDS-ON PARTNERSHIP
We take a hands-on, collaborative approach to identify solutions and potential new areas of improvement that align with your company’s vision.
ShieldWatch XDR is ShieldWatch’s Extended Detection and Response platform. It unifies real-time threat detection, response, and compliance monitoring into a single solution powered by AI, automation, and 24/7 SOC oversight.
It consolidates telemetry from endpoints, networks, cloud platforms, and user activity into a centralized platform for rapid detection and response.
ShieldWatch works with leading stacks including SentinelOne, CrowdStrike, Microsoft, Google, AWS, Slack, Teams, and email.
Expert analysts continuously monitor systems, investigate and validate threats, and provide proactive threat hunting and incident response around the clock.
Clients typically experience response times under three minutes, with automation and orchestration helping detect and contain threats before they escalate.