Your brand, not ours.
Deploy a fully white-labeled SIEM, XDR, and SOAR platform under your own name. Your clients see your logo, your support line, and your expertise — not a vendor they've never heard of.
Free 30-Day Trial
ShieldWatch gives your MSP a white-label SIEM, XDR, and SOAR platform backed by a real 24/7 SOC — so you can sell security under your own brand, with a team behind you that actually answers at 2 a.m. Why question the results? Try it for yourself!
GO FROM CYBER SECURITY TO CYBER MATURITY!
ShieldWatch is designed for organizations that want to elevate their cybersecurity delivery while focusing on client relationships and business growth.
Deploy a fully white-labeled SIEM, XDR, and SOAR platform under your own name. Your clients see your logo, your support line, and your expertise — not a vendor they've never heard of.
Alerts get triaged and escalated around the clock by a real security operations team, not a dashboard you have to watch yourself. You get the outcomes of a SOC without hiring or staffing one.
Onboarding, sales support, and technical training are built to help you stand up a real security line of business — not just resell technology and hope it sticks.
Turn security into a practice, not just a product. ShieldWatch's compliance tooling and guidance help you have the SOC 2, HIPAA, and cyber-insurance-readiness conversations your clients are already asking about.
Hover or click any feature to explore the full stack
Manage all clients from a single unified interface. Streamline operations, eliminate context-switching, and scale without adding headcount.
ShieldWatch’s comprehensive Extended Detection and Response platform is designed to unify threat detection, response, and compliance monitoring in one integrated solution. With a fusion of advanced AI-driven analytics, 24/7 SOC monitoring, and real-time orchestration capabilities, ShieldWatch empowers organizations to identify and neutralize threats before they can impact operations.

ShieldWatch XDR delivers a comprehensive security solution with everything you need to protect your organization.
Real-time monitoring of endpoints, cloud environments (MSFT, AWS, GCP), mobile devices, email, identity systems, and networks.
AI-powered threat telemetry and smart correlation detect and isolate threats across your environment before they escalate.
Systematic phone or text alerts to users, automated containment, and immediate forensics by our security analysts—powered by out-of-the-box playbooks and orchestration.
End-to-end visibility into workstations, servers, mobile devices, and cloud tenants—giving your organization full-stack control.
Set up in minutes. ShieldWatch automatically investigates up to 90 days of historical logs, immediately alerting you to any latent threats.
Our expert team stands ready 24/7 to review, triage, and respond to alerts, offering deep forensics and policy-level remediation.
ShieldWatch is designed for organizations that want to elevate their cybersecurity delivery while focusing on client relationships and business growth.
Expand beyond IT maintenance and network management to offer comprehensive managed security.
Deliver CMMC, HIPAA, SOC 2, ISO 27001, and NIST-ready security solutions as part of your compliance consulting services.
Strengthen your offerings with ShieldWatch’s AI-powered XDR and human-led SOC.
Offer ShieldWatch as a turnkey solution within your digital transformation or modernization projects.
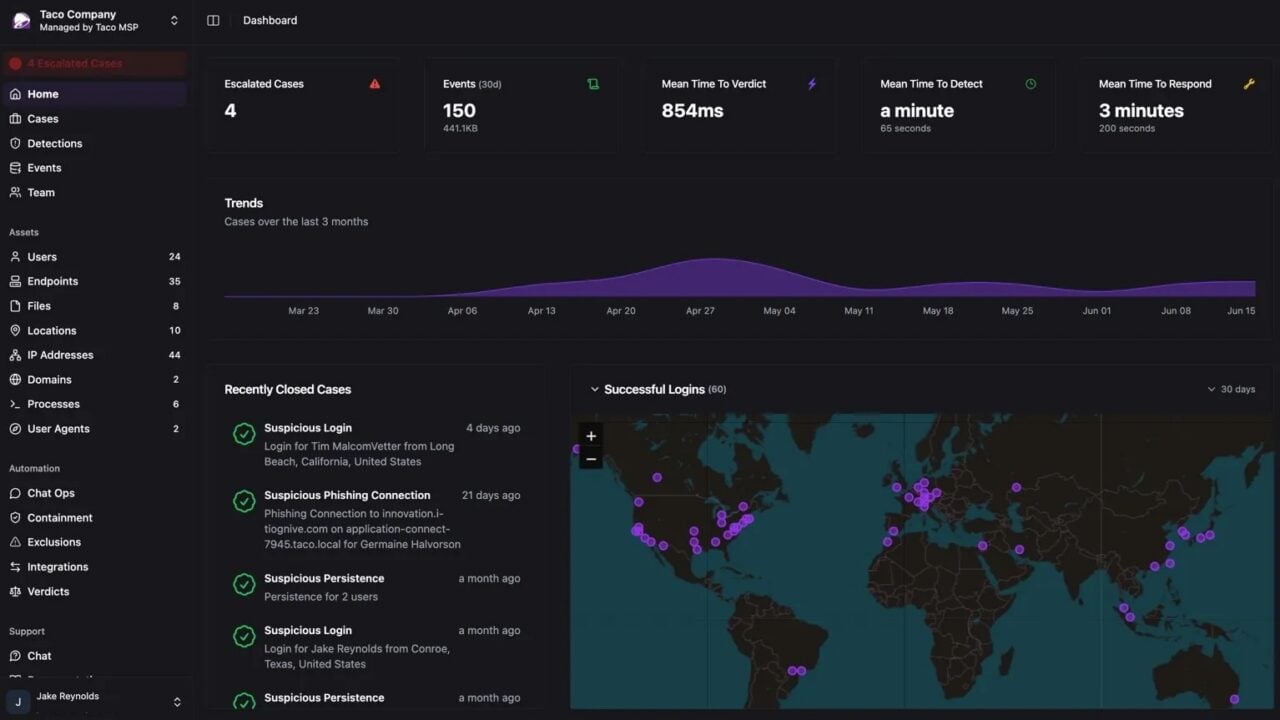
ShieldWatch XDR is ShieldWatch’s Extended Detection and Response (XDR) platform. It unifies real-time threat detection, response, and compliance monitoring into a single solution powered by AI, automation, and 24/7 SOC (Security Operations Center) oversight.
It consolidates telemetry from endpoints, networks, cloud platforms, and user activity into a centralized platform. This enables rapid detection of multi-vector threats and immediate response using automated containment and analyst-led investigations.
ShieldWatch works with leading tech stacks including SentinelOne, CrowdStrike, Microsoft, Google, AWS, and more. It also integrates with tools like Slack, Teams, and email via ChatOps to deliver alerts and responses in real time.
Our expert analysts continuously monitor your systems. When a threat is detected, we investigate, validate, and respond—not just alert. You’ll benefit from proactive threat hunting and incident response around the clock, across all time zones.
Clients typically experience response times under 3 minutes. ShieldWatch leverages automation and orchestration to detect and contain threats before they escalate, drastically reducing mean time to respond (MTTR).
